(Singapore, 03.11.2026)Cyber incidents involving European supermarket refrigeration systems, airline booking records and a Japanese cloud service offer a warning for Singapore, where businesses and daily services also depend on connected technology and external providers. The cases illustrate how security breaches can expose personal information, disrupt operations and cause financial losses.
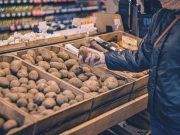
The latest disruption hit European supermarkets on 2 November, when an attack on refrigeration systems raised temperatures in fridges and freezers, forcing stores across several countries to throw away food.
According to Reuters, affected retailers included Ahold Delhaize and Colruyt in Belgium and Luxembourg, Swedish grocers ICA and Coop, Carrefour and Ireland’s Musgrave. IKEA also confirmed that one Belgian store had been affected.
At an ICA franchise store in Stockholm, sales manager Engla Ingwall said the attack occurred at about 2am but was discovered only hours later. She said the store’s freezers reached 50 degrees Celsius.
ICA confirmed that a limited number of stores had experienced an overnight incident affecting refrigeration and freezer systems.
In Belgium, butchery owner Luc De Laet said an employee alerted him at about 3.30am. When he arrived at his store south of Antwerp, he found refrigeration temperatures had risen as high as 18 degrees, ruining an estimated €15,000 worth of meat.
Refrigeration Attacks Force Retailers to Discard Food
The disruptions affected multiple retail networks. Musgrave said refrigeration systems at 13 SuperValu stores in Ireland were affected, prompting the removal of some chilled and frozen products from sale.
Carrefour reported problems at 15 of its 700 Belgian stores, while Colruyt said five shops had their refrigeration systems attacked. Sweden’s Coop reported unauthorised tampering with cooling systems at seven of its 800 stores.
The incidents followed an attack in France in October, when police said hackers took control of cooling units at hundreds of supermarkets, causing fires and food losses.
Some equipment affected in the latest incidents used temperature-control technology from Danish supplier Danfoss, which was also targeted in the French attack. The company said it had been working with customers to implement fixes.
European Agriculture Commissioner Christophe Hansen expressed concern about the repeated incidents, describing them as attempts to disrupt food supply chains and undermine consumer confidence.
No one had claimed responsibility, and investigators had not established whether the latest attacks were linked to those in France.
Tom Hegel, a researcher at cybersecurity firm SentinelOne, said retail chains operate extensive networks of refrigeration controllers, building management systems, access panels and payment equipment, creating numerous potential targets.
He said attacks of this kind could involve extortion, political motives or state-linked operations. The absence of financial demands in the recent cases could point towards sabotage, although responsibility and motive remained unconfirmed.
Airline and Cloud Breaches Expose Customer Information
Separately, a breach involving airline reservation-technology provider Amadeus has raised concerns about passenger information held by a shared supplier.
Malaysia Airlines said on 1 November that some customer information processed between August 2023 and September 2026 might have been affected. It was working with Amadeus and other relevant parties to investigate the incident.
The airline stressed that its own IT systems had not been breached and that there was no evidence financial information had been accessed. It advised customers to remain alert to suspicious communications requesting personal or financial details.
Other affected carriers included Japan Airlines, ANA, Cathay Pacific, Korean Air and Asiana Airlines.
Japan Airlines and its subsidiary Japan Transocean Air reported that about 92,000 customers were affected. Most exposed information consisted of names and flight details, although records for about 2,000 customers also included information such as passport numbers, nationality or contact details.
ANA reported approximately 37,800 affected customers, including around 1,700 whose passport or contact information might have been accessed alongside booking details. It said credit card numbers and passwords were not exposed.
Cathay Pacific reported that about 53,000 bookings were affected, generally involving booking references, passenger names and flight details. Some records might also have contained contact information, travel-document details or frequent-flyer numbers. It said there was no evidence financial or payment information had been accessed.
These figures cannot be combined into a confirmed passenger total because airlines used different counting methods and records could overlap.
Amadeus said it had identified a vulnerability affecting an environment used to display booking information, but did not provide a total number of affected customers. Airlines warned passengers about deceptive messages that could use genuine travel details to appear convincing.
In Japan, a separate attack on GMO Internet Group’s Onamae.com Desktop Cloud service exposed customer information and was linked to reports of unauthorised trading transactions.
GMO shut down the service on 21 October and later said about 27,000 servers might have been affected. Chief executive Masatoshi Kumagai apologised on 2 November and acknowledged that internal warnings about a systemic security weakness had not been adequately addressed. The company promised compensation and goodwill payments to customers.
Closer to Singapore, Malaysian Prime Minister Anwar Ibrahim warned Parliament on 3 November that Malaysia was among potential cyberattack targets, citing its expanding digital infrastructure and positions on international issues.
He said authorities were strengthening coordination and protection for strategic sectors, including energy, transport, finance and food supply. He proposed a closed-door briefing for lawmakers within the next one or two days, while declining to identify suspected attackers or specific targets publicly.